Portable Passmark OSForensics 11.1.1017 (x64) + WinPE
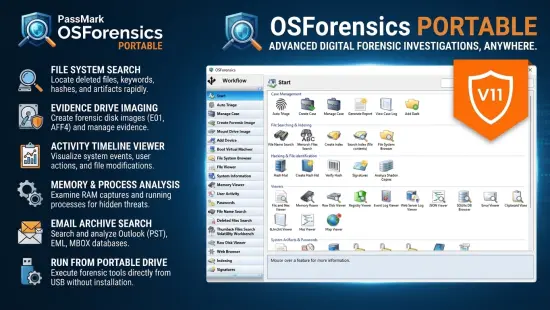
PassMark OSForensics Portable is a comprehensive digital forensics platform designed to help investigators, security professionals, IT administrators, auditors, and advanced users discover, analyze, recover, and organize digital evidence from computer systems and storage devices. Built with a wide range of forensic capabilities, the software provides a centralized environment for examining files, recovering deleted data, extracting valuable information, and generating detailed reports that support investigative workflows.
In today’s digital landscape, information is constantly being created, modified, transferred, and deleted. Whether an organization is conducting an internal investigation, responding to a security incident, performing compliance audits, or analyzing suspected unauthorized activity, having access to powerful forensic tools is essential. PassMark OSForensics Portable addresses these requirements by bringing together a collection of specialized modules that can efficiently process large amounts of data while maintaining a structured approach to evidence management.
The software is designed to provide investigators with fast access to critical information hidden within file systems, databases, emails, registry entries, system logs, internet activity records, and other sources of digital evidence. Through its intuitive interface and high-performance scanning engine, users can quickly uncover relevant artifacts and gain a clearer understanding of events that occurred on a target system.
Comprehensive Digital Forensics Platform
PassMark OSForensics Portable serves as a full-featured forensic environment that simplifies many tasks traditionally associated with digital investigations. Instead of relying on multiple standalone utilities, investigators can access a broad range of forensic functions from a single application.
The software supports both individual investigations and large-scale forensic projects. Evidence can be collected, categorized, analyzed, and reported while remaining organized within dedicated investigation cases. This structure helps maintain an efficient workflow and allows investigators to focus on interpreting evidence rather than managing multiple tools.
One of the most significant strengths of the platform is its ability to combine fast performance with detailed analysis. Users can index vast quantities of files, perform advanced searches, recover deleted information, and review system activity without constantly switching between applications.
High-Speed File Searching and Indexing
Searching for relevant evidence among millions of files can be one of the most time-consuming aspects of any digital investigation. PassMark OSForensics Portable addresses this challenge through its powerful indexing technology.
The application can create searchable indexes of storage devices and file collections, significantly reducing the time required to locate important information. Instead of scanning every file repeatedly, investigators can perform near-instant searches once indexing has been completed.
Advanced search filters allow users to narrow results based on file names, extensions, metadata, content, dates, sizes, and numerous other criteria. This capability is particularly useful when searching for specific documents, communications, keywords, or indicators of suspicious activity.
The software also supports complex keyword investigations, enabling users to identify patterns and relationships that might otherwise remain hidden within large datasets.
Efficient Case Management System
Digital investigations often involve multiple devices, evidence sources, reports, and findings. PassMark OSForensics Portable includes a dedicated case management system that helps investigators keep everything organized.
Each investigation can be stored within its own case, allowing evidence, notes, search results, bookmarks, and reports to remain grouped together. This structure simplifies collaboration and helps ensure that important findings remain linked to their originating investigation.
Case management functionality also supports easier documentation and reporting processes. Investigators can revisit previous findings, continue unfinished projects, and maintain consistent records throughout the entire investigative lifecycle.
The ability to centralize evidence analysis within defined cases contributes significantly to professional forensic workflows and helps maintain a clear audit trail.
Deleted File Recovery Capabilities
Deleted files frequently contain valuable evidence. Even when users intentionally remove information from a system, traces often remain on the storage device.
PassMark OSForensics Portable includes advanced recovery tools that help identify and restore deleted files from supported file systems. These capabilities can be invaluable when investigating incidents involving data theft, unauthorized activity, insider threats, or accidental data loss.
The recovery engine scans storage media for deleted file entries and recoverable data fragments. Recovered files can then be examined alongside other evidence collected throughout the investigation.
This functionality extends the investigator’s visibility beyond active files and provides access to information that users may have attempted to conceal.
Password Discovery and Security Analysis
Credentials often play a significant role in digital investigations. PassMark OSForensics Portable includes modules designed to locate stored passwords, authentication data, and encryption-related information.
The software can search systems for various password artifacts and credential remnants that may assist investigators in understanding user activity and account usage. Security analysts can leverage these capabilities when assessing system vulnerabilities, investigating breaches, or identifying unauthorized access mechanisms.
By discovering passwords and related information, investigators can often build a more complete picture of how systems were accessed and what actions may have occurred during specific events.
Detailed System Information Collection
Understanding a target environment requires access to detailed hardware and software information. PassMark OSForensics Portable includes comprehensive system information gathering tools that provide valuable insight into computer configurations and operating system details.
Investigators can review storage devices, installed applications, hardware specifications, network information, and numerous other system characteristics. This information can play an important role in establishing investigative context and understanding how specific systems were used.
Comprehensive system profiling also assists with incident response efforts by helping analysts identify unusual configurations, suspicious software installations, and potential indicators of compromise.
Registry Analysis for Forensic Investigations
The Windows Registry contains a wealth of forensic information that can reveal user activity, system configurations, software installations, and historical events.
PassMark OSForensics Portable provides specialized registry analysis tools that help investigators navigate and examine registry data efficiently. Important artifacts can be identified and analyzed without manually searching through thousands of registry keys.
Registry examinations can reveal evidence of application usage, connected devices, startup programs, user preferences, and countless other details relevant to digital investigations.
The software streamlines this process by presenting registry information in a structured and accessible format.
Email Analysis and Investigation Tools
Email remains one of the primary methods of communication in both personal and professional environments. As a result, email data frequently plays a crucial role in investigations.
PassMark OSForensics Portable includes capabilities for examining email archives and related artifacts. Investigators can search messages, identify relevant communications, and extract information that may support investigative findings.
The ability to analyze email content, attachments, and metadata allows users to reconstruct communication timelines and identify key interactions between individuals or organizations.
These features are particularly valuable in corporate investigations, compliance reviews, and cybersecurity incident response activities.
Browser and Internet Activity Examination
Internet activity often provides critical insight into user behavior and intent. PassMark OSForensics Portable offers tools designed to examine web browsing artifacts and related data.
Investigators can review browser histories, cached content, downloads, cookies, and other internet-related artifacts. This information can help establish timelines, identify accessed resources, and reveal patterns of online activity.
By analyzing browsing behavior, investigators can uncover relevant evidence regarding research activities, downloads, communications, and interactions with online services.
This capability is especially useful when examining potential policy violations, security incidents, or cases involving unauthorized access.
Memory and Live System Analysis
Some forms of evidence only exist while a system is running. PassMark OSForensics Portable supports analysis activities that can help investigators capture and examine volatile information before it disappears.
Memory-related analysis can provide insight into running processes, active connections, loaded modules, and other transient system artifacts. Such information is often essential when investigating malware infections, intrusion attempts, and advanced cyber threats.
The ability to analyze both static and live evidence broadens the scope of digital investigations and allows analysts to obtain a more complete understanding of system behavior.
File Signature Verification and Hash Analysis
Maintaining evidence integrity is a critical component of digital forensics. PassMark OSForensics Portable includes hash analysis capabilities that support evidence verification and file identification.
Users can generate and compare hash values to confirm file authenticity and detect modifications. Hash matching also helps investigators identify known files, reduce redundant analysis efforts, and focus attention on suspicious or unknown items.
This functionality is commonly used to validate evidence, verify forensic images, and compare files against trusted or investigative reference collections.
Hash-based analysis enhances both efficiency and reliability throughout the investigative process.
Disk Imaging and Evidence Preservation
Proper evidence acquisition is fundamental to forensic investigations. PassMark OSForensics Portable provides imaging tools that help create forensic copies of storage media while preserving important data.
Forensic imaging allows investigators to work with duplicate copies rather than original storage devices. This approach minimizes the risk of evidence alteration and supports best practices for evidence handling.
Disk images can be analyzed using the software’s numerous forensic modules, providing flexibility and convenience throughout the investigative lifecycle.
The imaging capabilities contribute to evidence preservation and support responsible forensic examination procedures.
Advanced File System Exploration
PassMark OSForensics Portable offers detailed access to file system structures, enabling investigators to explore storage devices at a deeper level.
Users can browse directories, inspect metadata, recover hidden information, and locate artifacts that may not be easily accessible through standard operating system tools. The software supports examination of various storage formats and file systems, increasing its effectiveness across diverse investigative scenarios.
This deep visibility helps analysts discover evidence that may otherwise remain unnoticed, particularly when dealing with deleted, hidden, or obscured information.
User Activity Reconstruction
A central objective of many investigations is determining what actions were performed on a system and when those actions occurred.
PassMark OSForensics Portable helps reconstruct user activity by gathering and analyzing artifacts from numerous sources. These artifacts may include application usage records, system logs, browser histories, document access records, and other indicators of user interaction.
By correlating information from multiple sources, investigators can build detailed timelines and identify meaningful behavioral patterns.
Timeline reconstruction assists in validating investigative hypotheses and establishing chronological sequences of events.
Database and Structured Data Analysis
Modern applications frequently store information within databases rather than traditional files. PassMark OSForensics Portable includes functionality for examining structured database content and extracting relevant records.
Investigators can review application data, configuration information, user-generated content, and other stored records that may contain important evidence.
Database analysis can be especially useful when examining messaging platforms, business applications, browsers, and software products that rely heavily on structured storage systems.
The ability to access and interpret database information expands the range of evidence available to investigators.
Reporting and Documentation Features
Effective reporting is essential in every investigative process. PassMark OSForensics Portable includes reporting capabilities that allow investigators to document findings in a professional and organized manner.
Reports can incorporate evidence summaries, search results, recovered files, screenshots, timestamps, and analytical observations. These reports help communicate findings to stakeholders, management teams, legal professionals, and other interested parties.
Well-structured reporting simplifies evidence presentation and supports transparency throughout an investigation.
The integrated reporting tools save time and help ensure consistency in documentation practices.
Suitable for Multiple Professional Environments
PassMark OSForensics Portable is versatile enough to address the needs of numerous professional fields.
Common usage scenarios include:
- Corporate internal investigations
- Cybersecurity incident response
- Data breach analysis
- Compliance auditing
- Fraud investigations
- Academic research
- Law enforcement support
- IT administration
- Risk management
- Security consulting
Its broad feature set makes it valuable for organizations seeking a unified forensic analysis solution without requiring multiple separate applications.
Performance-Focused Investigation Workflow
Large-scale investigations frequently involve hundreds of gigabytes or even terabytes of data. PassMark OSForensics Portable is engineered to help investigators process substantial amounts of information efficiently.
Fast indexing, optimized searching, structured evidence organization, and comprehensive analysis tools combine to improve productivity throughout investigative workflows.
Instead of spending excessive time locating information, users can focus on interpretation, validation, and decision-making activities that produce meaningful investigative results.
The result is a platform that balances depth, speed, and usability for both experienced forensic professionals and users entering the field of digital investigations.
Features at a Glance
- Comprehensive digital forensics platform
- High-speed file indexing and searching
- Advanced keyword investigation tools
- Case management system
- Deleted file recovery
- Password discovery capabilities
- System information collection
- Registry analysis tools
- Email investigation features
- Browser activity examination
- User activity reconstruction
- Forensic disk imaging
- Evidence preservation workflows
- Hash verification and comparison
- File signature analysis
- Database inspection utilities
- Memory analysis support
- Timeline creation and event correlation
- Advanced file system exploration
- Reporting and documentation tools
- Support for multiple storage devices
- Investigation bookmarking and evidence organization
- Security incident response capabilities
- Compliance and audit investigation support
- Professional forensic reporting environment
Changelog
- Updated OSFMount to version 3.2.1000.
- Fixed a crash that could be triggered by a corrupt or empty case device metadata file during case loading.
- Modified subscription expiration handling so the end date is applied at the end of the day.
- Fixed possible crashes when adding physical disk devices.
- Fixed potential issues when loading invalid or corrupted case devices.
- Corrected Office decryption behavior when running multiple instances on the same file.
- Fixed invalid time zone data during disk image or drive letter scanning.
- Resolved Linux dpkg.log parsing issues involving empty files.
- Fixed Jump Lists extended information parsing problems.
- Improved drive insertion responsiveness.
- Updated DirectIO driver with security-related improvements.
Download OSForensics Portable
Filespayout – 306.1 MB
RapidGator – 306.1 MB